
VITON13 / Focused service
Web application security hardening
Reduce practical account, data and deployment risks through prioritised fixes your team can maintain.
Get an estimate in 1 working day↘Written estimate within 1 working dayIn short
What does Web application security hardening include?
Web application security hardening starts at USD 73 with AI-assisted production or USD 93 with a human-led route; typical delivery is 5–8 working days.
The published scope includes threat and access review, prioritised security fixes, verification and response notes.
Includes 2 revision rounds on the deliverables; VITON13 confirms the scope in writing.
What you get and on what terms
Web application security hardening
AI-assistedfrom $73
Human-ledfrom $93
- Threat and access review
- Prioritised security fixes
- Verification and response notes
- Timeline
- 5–8 working days
- Revisions
- 2 rounds on the deliverables
- Included
- only the deliverables listed in the agreed package
- Not included
- external costs and work outside the agreed scope
- From you
- brief, current materials and any access needed for this scope
- You receive
- listed deliverables plus a written completion note
Prices in USD; other currencies are approximate. Scope, revisions and dates are written into your estimate.
Work
Cases
INTERNALOur own product
VITON ID and the personal cabinet
Account & cabinet · 2026
VITON ID is the account behind viton13.com: one sign-in for orders, service conversations with the studio and VITO bonuses, plus a console for admins. Files attached to a studio order are encrypted in the browser before upload.
Read the case →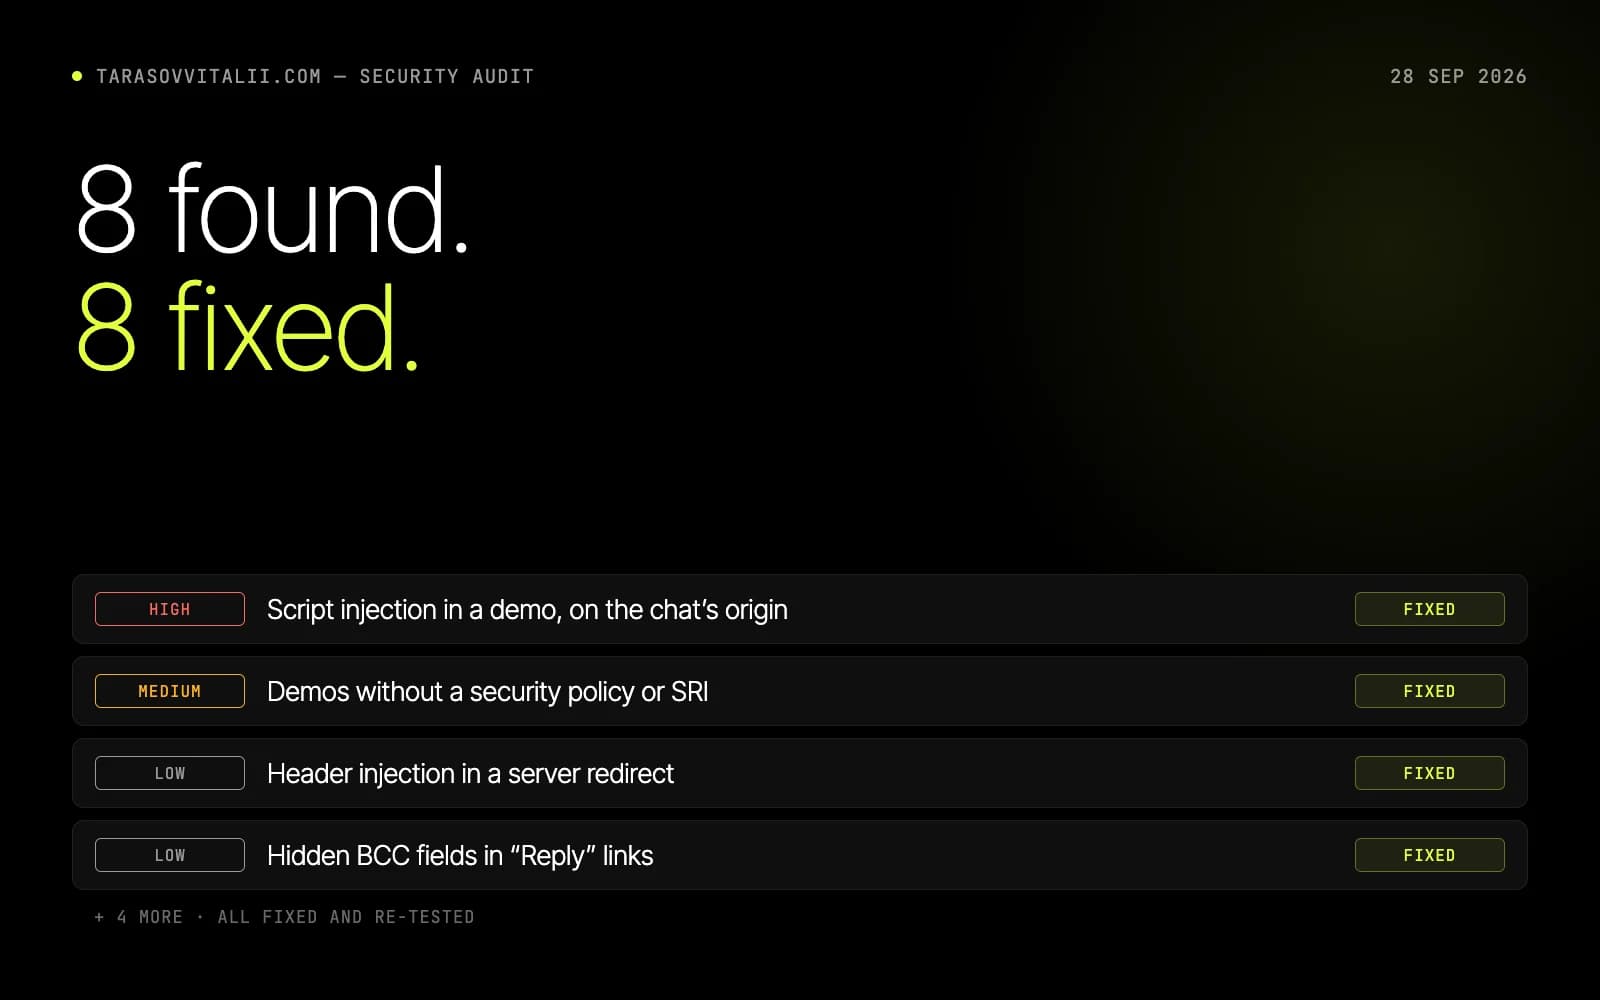
INTERNALOur own product
tarasovvitalii.com security audit
Security audit · own site · 2026
A white-box security review of the founder’s portfolio site, tarasovvitalii.com: its chat, its message API, its server and 15 concept demos. We found eight issues, one of them high-risk script injection on the origin where the chat keeps its sign-in session, fixed all eight and re-tested every fix.
Read the case →Related guides
All guidesYOUR NEXT PROJECT · DEVELOPMENT FROM $13
From an idea to a clear plan.
Explore the scope and starting cost, then talk directly with VITON13. Your selected service stays with the conversation. Written estimate within 1 working day.
Let’s make it yours.
Explore our work or bring your own idea. It starts with a conversation.
Concept↗
Concept site · WebGL · English · 2026HYPERSOLID
Scope and pricingYou can choose later+
01 / Scope & estimate
Web application security hardening
Starting budgetFrom $73
Reduce practical account, data and deployment risks through prioritised fixes your team can maintain.
Inside this scope
- Threat and access review
- Prioritised security fixes
- Verification and response notes
- Timeline: 5–8 working days
- Revisions: 2 rounds on the deliverables
- Included: only the deliverables listed in the agreed package
- Excluded: external costs and work outside the agreed scope
- Input required: brief, current materials and any access needed for this scope
- Handoff: listed deliverables plus a written completion note
A starting estimate for the selected scope. We confirm deliverables, timing and the final price in writing before work starts. External costs are separate.
What you can count on
- Written estimate within 1 working day, sent to the contact you choose.
- Scope in writing before work starts: deliverables, revision rounds and what is not included.
- We work in four languages and show prices in your currency.
- No account needed. Attachments are encrypted in this browser before upload.
Send a detailed brief or attachments
Development from $13
AI reduces repetitive production time. VITON13 passes that efficiency back to the client while human review remains part of every delivery.
Order with VITON IDHow the work is set up
01
The business problem — Threat and access review
Web application security hardening becomes relevant when a concrete workflow, decision or handoff can no longer be trusted. Reduce practical account, data and deployment risks through prioritised fixes your team can maintain. We begin with the blocked action and its operational cost, then choose only the technology needed to remove that constraint. For Web application security hardening, the opening workshop uses a real blocked case and its accountable owner rather than a fictional product brief.
02
What the build covers — Prioritised security fixes
For Web application security hardening, the build boundary joins Threat and access review, Prioritised security fixes, Verification and response notes. Adjacent features stay outside until they have their own owner, data source and acceptance condition, so a focused commission cannot quietly become a platform rewrite. The evidence chain must connect Threat and access review to Prioritised security fixes; if that link cannot be demonstrated, Verification and response notes is not ready for acceptance.
03
Risks to resolve early — Verification and response notes
The failure to expose early is adding tools without a release threat model, test ownership, alert response and a rollback that the team has actually rehearsed. The route-specific failure appears when Prioritised security fixes changes state but Threat and access review cannot prove the input and Verification and response notes cannot reconstruct what happened. The hardening review ties one threat to an exposed asset, permission boundary, exploit test, fix and retest evidence. We turn that risk into a test case or operational checkpoint instead of burying it in a generic “QA included” line. Threat and access review is treated as an operating component, Prioritised security fixes as the controlled handoff and Verification and response notes as the record a future maintainer can inspect.
04
How delivery is approved — Threat and access review
The page is not accepted because a demonstration looks polished. Acceptance means a controlled change fails visibly, protects critical data and can be reversed from the written runbook. Sign-off requires one normal and one failed trace across Threat and access review, Prioritised security fixes and Verification and response notes. Representative content, permissions, error states and recovery are exercised before the release is called complete. A failure exercise begins at Prioritised security fixes, follows the affected user or operator back to Threat and access review, and verifies recovery through Verification and response notes.
05
Life after release — Prioritised security fixes
Web application security hardening continues after deployment through ownership, monitoring, maintenance and a usable handover. The final package records access, dependencies, known limits and the action to take when the normal route fails. The buy-versus-build comparison is written specifically around ownership of Threat and access review, continuing operation of Prioritised security fixes and portability of Verification and response notes.
06
How the quote is formed — Verification and response notes
Web application security hardening starts at $73 with a usual window of 5–8 working days. That published entry point remains valid for the stated outputs; integrations, migrations or risk controls outside them are estimated separately before approval. The final review does not ask whether web application security hardening looks complete; it asks whether Threat and access review, Prioritised security fixes and Verification and response notes survive the agreed representative case.
Threat and access review
Threat and access review is the working artifact used with a representative input. Its owner and expected state are named before production, so approval cannot depend on a polished demo.
Prioritised security fixes
Prioritised security fixes carries the controlled transition. We exercise one normal path and one interruption against this risk: adding tools without a release threat model, test ownership, alert response and a rollback that the team has actually rehearsed. The route-specific failure appears when Prioritised security fixes changes state but Threat and access review cannot prove the input and Verification and response notes cannot reconstruct what happened. The hardening review ties one threat to an exposed asset, permission boundary, exploit test, fix and retest evidence.
Verification and response notes
Verification and response notes is the handover and proof layer. A second authorised maintainer must be able to reproduce the result and verify a controlled change fails visibly, protects critical data and can be reversed from the written runbook. Sign-off requires one normal and one failed trace across Threat and access review, Prioritised security fixes and Verification and response notes.
Read the full guide before ordering
Web application security hardening — implementation checklist
Plan Web application security hardening from the first working Threat and access review through Prioritised security fixes to an operable Verification and response notes.
Open the article↗Questions people ask before buying
01What evidence should exist before the work starts?+
Bring one normal example, one failed example, the current stack, access constraints and the person who will accept the result. That is enough to expose unknowns without pretending the whole specification is finished. For Web application security hardening, the opening workshop uses a real blocked case and its accountable owner rather than a fictional product brief.
02What is the acceptance test?+
Acceptance is not a presentation. For this service it means a controlled change fails visibly, protects critical data and can be reversed from the written runbook. Sign-off requires one normal and one failed trace across Threat and access review, Prioritised security fixes and Verification and response notes, using representative data, permissions and at least one failure state. The evidence chain must connect Threat and access review to Prioritised security fixes; if that link cannot be demonstrated, Verification and response notes is not ready for acceptance.
03Which risk changes the scope most?+
The decisive risk is adding tools without a release threat model, test ownership, alert response and a rollback that the team has actually rehearsed. If it cannot be tested safely, the proposal must include discovery, a pilot or a smaller boundary before production. Threat and access review is treated as an operating component, Prioritised security fixes as the controlled handoff and Verification and response notes as the record a future maintainer can inspect.
04Could an existing tool do this instead of a custom build?+
Sometimes. We compare the requested ownership with a focused remediation lane instead of replacing the whole platform or security stack. If Prioritised security fixes can remain in the current stack, commission only the missing ownership and verification layer. Custom work is justified only when the operating difference matters more than the continuing complexity. A failure exercise begins at Prioritised security fixes, follows the affected user or operator back to Threat and access review, and verifies recovery through Verification and response notes.
05How are price and timing confirmed?+
The published entry point is $73 and 5–8 working days for the listed outputs. Dependencies outside that boundary are priced before approval. The buy-versus-build comparison is written specifically around ownership of Threat and access review, continuing operation of Prioritised security fixes and portability of Verification and response notes.
What clients say
More in this category
Web accessibility remediation
Remove the code, content and interaction barriers that prevent people from completing important routes.
↗
AI-generated code rescue
Stabilise an AI-built codebase by reproducing failures, protecting critical routes and replacing unsafe assumptions in controlled increments.
↗
QA and test automation
Catch critical regressions before customers do with a focused automated release safety net.
↗
AI web application development
Turn a useful AI workflow into a secure product with owned data, review points and measurable output.
↗